

Authored By: Fernando Ruiz
McAfee’s Mobile Research Team identified more than 1,900 unique applications associated with the campaign across over 500,000 devices in more than 190 countries. Based on publication patterns, we estimate that the operators were releasing approximately 20 to 25 new applications per day, each leveraging different themes, brands, and impersonation targets. The highest concentrations of affected devices were observed in India, Russia, and the United States.
Most of these apps were published on the official android platform impersonating well-known products such as CapCut, Roblox, Zelle, PayPal, Netflix, Xbox Game Pass, Siri, iMessage, etc. under different developer accounts, they shared a common codebase, repeated the same deceptive behaviors, and contacted the same remote server, which told each app where to send its users. That destination was an advertising funnel and in our testing the ads it served led to third-party subscription-fraud pages billing as much as $49.99 per month
McAfee identified the malicious apps, conducted technical analysis, and reported its findings to Google through responsible disclosure channels. Following McAfee’s report, Google removed all of the identified apps from Google Play. McAfee is a member of the App Defense Alliance, which supports collaboration across the mobile ecosystem to improve user protection. McAfee Mobile Security detects these apps as a Medium-Risk Threat. For more information, and to get fully protected, visit McAfee Mobile Security.
The Financial Impersonators
We identified fake apps impersonating Zelle, PayPal, Apple Pay, Mir Pay, Binance and several banks. One fake PayPal app had been downloaded 10,000+ times.
Zelle has no standalone consumer app: it lives inside your bank’s app so anyone searching Google Play for “Zelle” is already confused. And Apple Pay has no Android app at all, so users searching for it cannot find a legitimate result. Both are searches with no correct answer, which makes them ideal traffic to intercept.
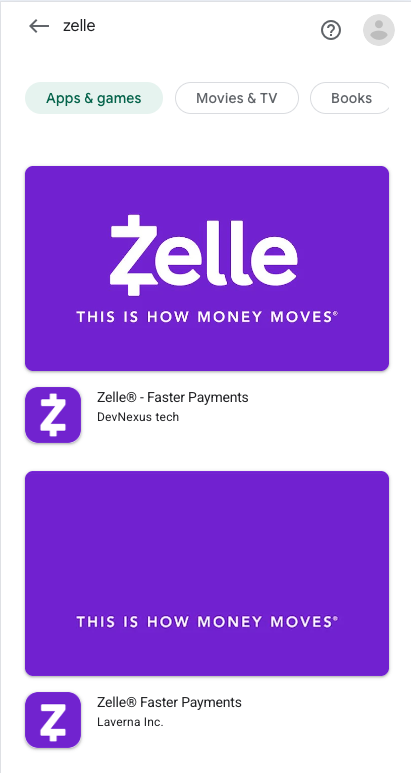
Figure 1: Firsts result on Google Play of ‘Zelle’ search are Fake Applications
Combine that with an in-app browser whose address bar is hidden and whose destination the operator controls remotely, and the risk profile of a fake banking app is simply not the same as a fake video editor even when both currently do nothing worse than show ads.
From the user’s perspective the current risk is straightforward: they search Google Play for “Zelle”, the first results include fake apps, and installing it delivers not a banking guide but a stream of full-screen ads. Tapping one leads to a page requesting their credit card details for a “free” trial that then bills them monthly.
What Users Actually Got: Gambling Inventory, on an “Everyone” Rating
In multiple cases we observed a gambling-style quiz funnel: “Win Mega Jackpot,” “50,000 COINS DAILY,” “PLAY FOOTBALL QUIZ,” “Play Now.”
Now consider who was looking at those store pages: Among the apps still available for measurement at the time of our analysis, the ones impersonating children’s and teenagers’ brands had been downloaded more than 86,000 times:
| Downloads | App title | Package Name |
|---|---|---|
| 50,000+ | Roblox | com.sitaram.robloxgame1 |
| 10,000+ | Roblox | com.sitaram.robloxgame3 |
| 10,000+ | Netflix Game Controller | netflixgamecontroller.uzair1 |
| 10,000+ | Netflix Game Controller: Play | netflixgamecontroller.uzair2 |
| 5,000+ | Xbox Game Pass: Play Games | xboxgame.abdul2 |
| 1,000+ | Fall Guys for Mobile | com.react.fallguysgame1 |
Across the full campaign we identified 37 apps impersonating games and services aimed at young players: Roblox, Minecraft, Fall Guys, Brawl Stars, Clash of Clans, Deltarune, Xbox Game Pass even GTA VI.
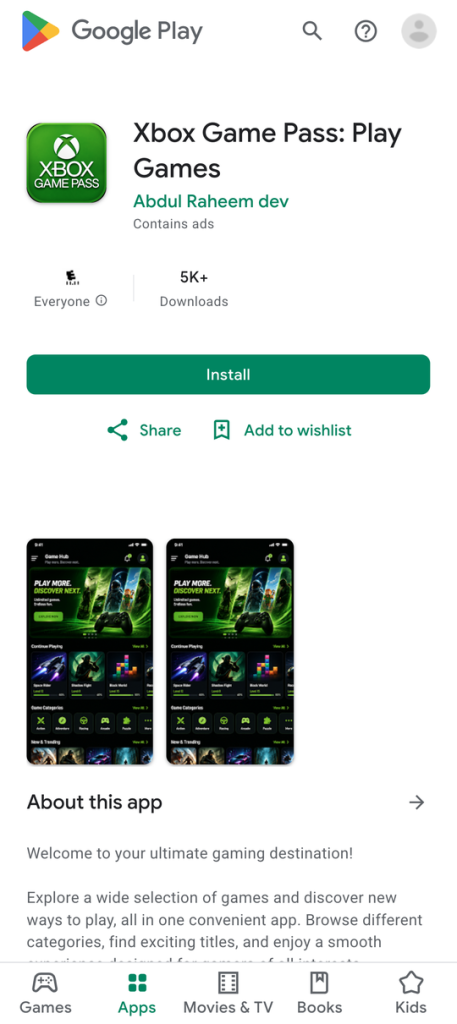
Figure 2: Fake Xbox App with over 5,000 installations
Every one of these listings carried an “Everyone” content rating.
So, the chain runs: a child searches Google Play for Roblox, installs an app called Roblox with the Roblox logo, rated suitable for everyone — and is funneled into gambling-style prize inventory that the operator can redirect at will. No exploit, no permission prompt, no warning.
The Searches With No Correct Answer
One application captured this strategy particularly well: Published as “AppStore: App Downloader,” the application used a legacy Appstore icon and presented itself as an Android version of Apple’s official software marketplace.
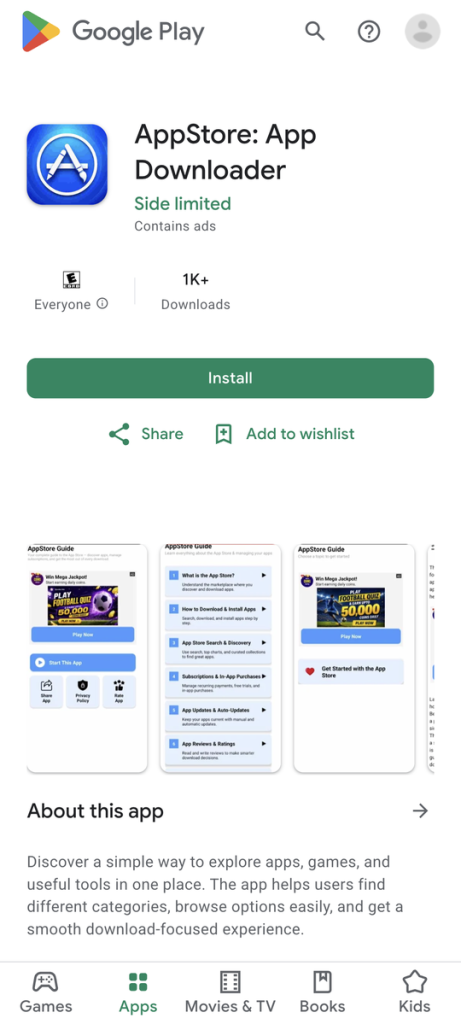
Figure 3: Fake AppStore on Google Play with over 1K Downloads
A legitimate Apple App Store cannot exist on Android because Apple operates the App Store exclusively for its own platforms, and the iOS applications it distributes are not compatible with Android’s operating system or application format. Any Android app claiming to be Apple’s App Store is therefore impersonating the service rather than providing the official marketplace.
“AppStore: App Downloader” was not an alternative marketplace but an advertising funnel disguised with Apple’s branding, rated for all users, and distributed through Google Play.
There is no App Store, Siri, iMessage, FaceTime nor Apple Pay app for Android. Zelle has no standalone consumer app, it lives inside your bank app. Every one of those is a search people perform on Google Play every day, and every one of them is a search with no legitimate result.
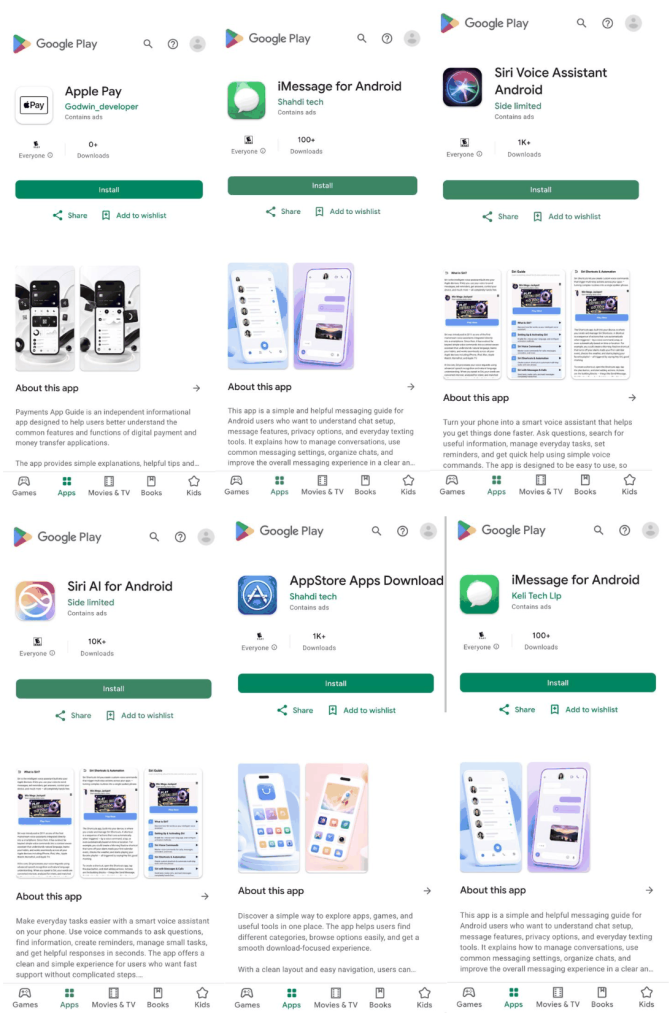
Figure 4: Multiple fake apps that does not officially exist on Android
The user’s own intent is the vulnerability: they want the thing, they cannot have the thing, and something appears that looks exactly like the thing. No security control mediates that moment. It is not a technical failure at all: it is a person trusting a logo, which is precisely what logos are for.
How Are the Ads Displayed?
Each app is a shell. It wears the branding of something people search for — CapCut, Roblox, Zelle, PayPal, Netflix, Huawei Health, Xbox Game Pass, Siri, iMessage — and behind that branding it contains no real product. What it contains is a redirector.
On launch, the app contacts a server controlled by the operator:
`hxxps://rewadevelopments[.]online/data/.json`
The server replies with a small configuration block. One field in that block, `qureka_url`, holds a web address. The app takes that address and opens it in an in-app browser window, a Chrome Custom Tab, configured with the URL bar hidden.
In every case we observed, the address served was a gambling-style quiz site promising daily coin rewards. Users did not get a CapCut tutorial or a Zelle guide. They got an endless funnel of ad and quiz pages, monetized by the operator.
The mechanism matters more than today’s payload. Because the destination is fetched from the server at every launch, the operator can change where these apps send users at any moment, for any single app, without shipping an update and without passing store review again. An app wearing a bank’s logo, opening a browser window with the address bar hidden, pointed wherever the operator chooses, is a capability that can be used for phishing and credential exfiltration.
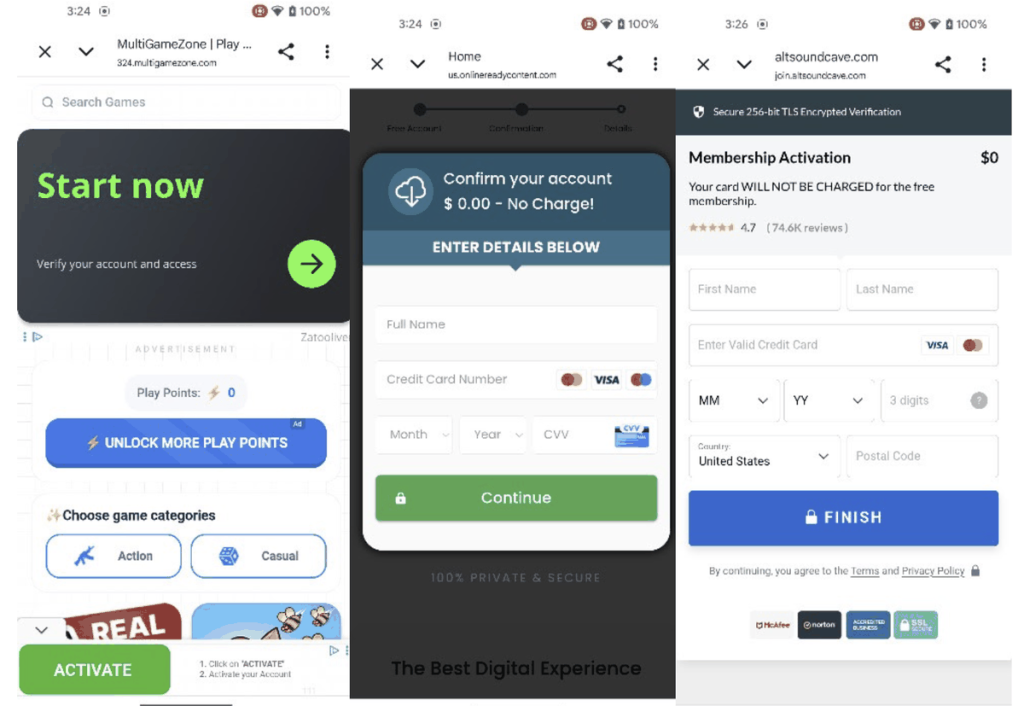
Figure 5: Ads severed from the website loaded in full screen that funnel to subscription fraud.
The full-screen ads users encounter are not served by the app. Its own ad slots are configured with Google’s public test IDs, which generate no revenue — so the app earns nothing from advertising itself. The ads come from the website the app opens: the destination supplied in the remote JSON configuration. That page’s ad inventory is filled with deceptive offers which, when tapped, lead to credit-card forms tied to subscription-fraud billing.
What Makes These Apps Interesting Is What They Do Not Do
There is no exploit, privilege escalation, rooting attempt, dynamic code loading, obfuscation, encrypted payload, or dropper chain. The applications request no dangerous Android permissions. From the perspective of conventional static analysis, their code presents few of the indicators typically associated with Android malware.
This campaign avoids many of those controls because its primary deception occurs outside the application code. Rather than exploiting a software vulnerability, the operators exploit the user’s trust in an official app store and in recognizable brands.
The post-installation behavior can remain technically simple, as it does here with advertising redirection, because persuading the user to install the application is the most critical stage of the operation.
The affected users did not need to follow a malicious link or sideload an APK from an unofficial forum. They searched an official application store for a product they recognized, and the search results presented an application with the expected name, logo, and visual identity.
How to protect yourself
- Install financial apps only from your bank’s own website or a verified link. If you are searching for an app store for a payment brand, you are in the exact position this campaign targets.
- Be suspicious of “guide,” “tutorial,” “helper” and “tips” apps for products you already use.
- Legitimate services do not need a third party to explain them.
- Check the developer’s name, not just the app name and icon. A real brand’s app is published by that brand.
- If a product doesn’t exist on your platform, no app can provide it. There is no Apple Pay, Siri, or iMessage for Android.
- Ignore install counts as a trust signal. Several of these apps had tens of thousands of downloads.
- Run mobile security software. McAfee Mobile Security detects this family.
Conclusion
Mobile security has genuinely improved. Permissions are narrower, sandboxing is stronger, exploit mitigations are routine, store review catches more than it used to, and AI now finds obfuscated payloads at a scale no human team could match. Every one of those defenses works but none of them was tested here.
Attackers move to one part of the system that cannot be patched: the judgment of the person holding the phone. And they apply pressure exactly where that judgment is weakest — a familiar logo, an official store, a name that matches what you searched for.
These apps are adware or a medium risk threat rather than malware because the fraudulent content is not theirs. The app opens a web page chosen by its operator; that page’s advertising slots are filled by open programmatic ad exchanges, which sell to whichever advertiser bids. The subscription-fraud pages belong to those advertisers.
As threat actors continue to exploit trust rather than software vulnerabilities, McAfee remains committed to protecting users, raising awareness, and collaborating across the industry to ensure that seemingly harmless applications do not evolve into large-scale fraud operations.
IOC
Prevalent Apps
| App title | Package | Play downloads | SHA-256 (primary build) |
|---|---|---|---|
| Roblox | com.sitaram.robloxgame1 | 50,000+ | 4f7b36963518e701276c77c1cad88d16fe64e8025c5223141c9af0eeb954ea63 |
| Roblox | com.sitaram.robloxgame3 | 10,000+ | c56d49a2f323ca0333778964fd58a7399aa60c8136a6a178adc1f222747b353f |
| Netflix Game Controller | netflixgamecontroller.uzair1 | 10,000+ | 2bdbd5c78a9d08b69983b965ae466210329b09eb26e5b491acdae9b822c729ab |
| Netflix Game Controller: Play | netflixgamecontroller.uzair2 | 10,000+ | 8cf714e0dab975c12cb5ac16837d7d2748a7f1672a3210a0e8e247dc405f8c68 |
| Xbox Game Pass: Play Games | xboxgame.abdul2 | 5,000+ | 37539a20f07bd29e9285e7266ab29015c5467241bea43eee48f77769c42bbc7e |
| Fall Guys for Mobile | com.react.fallguysgame1 | 1,000+ | d9ae6d844bf9269bee7d1f67f2f3d9e1d932974733068639c7204c2c92c391b1 |
| Capkut – Video Editor | com.flintos.capcut2 | 50,000+ | ba7a00fd597c04b7aa2efb59da853b1fcf34ba3bb63e7fbef2b9d9ef1a497641 |
| Capcut Video Editor 2026 | com.capcut.capvideoeditorapp58 | 10,000+ | 9b9e08b176d12c5e388b33c3e1fcdf2ba52b94cc6b310b56e3596eb783c26569 |
| Siri Voice Assistant Android | com.shahdi.siri2 | 10,000+ | b015de54db5073758909e5f3eaa90e73d7ff6f923195569d22395808b99a5557 |
| Siri for Android | com.shahdi.siri1 | 5,000+ | 9a0881a67a7c35592216e0896e184d1ed960ef5c2280a6dafcfcbc0dcb29c099 |
| Siri for Android | com.keli.siriapp1 | 1,000+ | 30a9f7461a0c11061b9349004f3dcd39ec763ec8bf1520ce655653fca67e183e |
| iMessage for Android | com.keli.imessage3 | 100+ | ac46add9b7bb09779ab0a51924601e649431153c40d95c2ecc995e614ff2b89d |
| iMessage Android App | com.shahdi.imessage2 | 100+ | 83a95ceb22e24d5486f997d3ab7a8fa336cbf52c6489bfd20b285ccb16237f8e |
| Apple Health for Android | com.godwin.applehealth2 | 1+ | 5d2c823acf6e719553688626a113e79842d186de7d3203c011b032eb2f87adca |
| Huawei Health | huwaei.health1 | 10,000+ | 695eca22217b60b6218fbef51bcf660e569f7ce36c1d73a4646494d5489ae352 |
| Casino Plus PH | casinoplus.pindo3 | 10,000+ | 3a50fa0ee7be36cbb1052254fbfdc0602abd7f52d69d7dc32d5c9ea6148ed16c |
| Aviator Game | com.aviator.aviatorgamejamantech2 | 1,000+ | 18af2b9a1e9db5f85c789252dbb0048a244e0a181f88b31c0969e6789b9657b8 |
| GTA VI | com.react.gta6game1 | N/A | 78a098470a7926dc0bd36c625032fd421587aea88200fdbb877dbc655110c5f5 |
Financial Impersonators
| App title | Package | Play downloads | SHA-256 (primary build) |
|---|---|---|---|
| PayPal – Fast Payments | com.paypal.wallawalled11 | 10,000+ | 601639168ac739e08fd267e86ba7eae440116e5b295fe01c00098bc2d9845405 |
| Zelle® Easy Secure Payments | com.premkumar.zelleapp5 | 100,000+ | 8a943f50417c53fd9d8f522fdb69d76c96ca386c2416a43d20f9181350282bd1 |
| Zelle® Faster Payments | com.premkumar.zelleapp2 | 50,000+ | 84fac9f350cd9d627392125cd3b06bac62321a2a36954605bd4680383ee86ae2 |
| Zelle® – Faster Payments | com.zelleapp.devnexus2 | 10,000+ | 99122b355ba17d6fa55625414f9a48f8755f4a438374ce85c73c751e9f4fe6b6 |
| Zelle® – Online Payments | com.mhd.zelleapp2 | N/A | 0022360894f15199c5f2fda5b5d8be3d26045d12ad50d80d02a23741601345af |
| Apple Pay | com.godwin.applepay3 | N/A | aa6883d64438a4374a5f44b5180d8ff12ca3d0c9423946df092420291007fdaf |
Stay Updated
Follow us to stay updated on all things McAfee and on top of the latest consumer and mobile security threats.